

The Weaponization of Intelligence: AI Agents, Deepfakes, and Integrity
The risks facing organizations in 2027 will look very different from those of today. Join us for 2026 Fall Threat Horizon Forum, an executive-focused discussion exploring how rapid digital acceleration is colliding with growing geopolitical, economic, and technological uncertainty. We'll examine the weaponization of intelligence through AI agents, deepfakes, executive impersonation, and unmanaged agentic AI sprawl, while also addressing the security challenges emerging across extended digital ecosystems, including software supply chain vulnerabilities, third-party exposure, and the race to prepare for a post-quantum world. The conversation will then shift from defense to resilience, covering cyber-enabled fraud, board-level accountability, business continuity, and the growing need to unify disaster recovery with cyber incident response. You'll leave with a practical framework outlining what boards and executive leaders should prioritize immediately to move beyond "keeping the lights on" and transform security into a strategic resilience enabler.
Registration form below
Agenda & Presenters
| Welcome & Opening Keynote | The 2027 Risk Horizon: Navigating the Intersection of Growth and Volatility Setting the stage for how digital acceleration intersects with systemic global fragmentation. |
| Power Sessions | The Weaponization of Intelligence: AI Agents, Deepfakes, and Integrity Covering AI-enabled threats, unmanaged agentic AI sprawl, deepfake executive impersonation, etc. |
| Fireside Chat / Data Briefing | Securing the Extended Ecosystem: Supply Chains, Software Integrity, and the Quantum Clock Addressing generative code supply chain flaws, third-party digital exposure, and preparing for post-quantum cryptographic migration. |
| Networking Break | Coffee, Snacks, Beverages |
| C-Suite Panel Discussion | From Defense to Resilience: Redefining Fraud, Liability, and Business Continuity Focusing on cyber-enabled fraud, board-level regulatory accountability, and unifying disaster recovery with cyber incident response. |
| Closing Keynote | The Securing 2027 Blueprint: What Boards and Executives Must Do Monday Morning Actionable takeaways on shifting from security keep the lights on to strategic resilience enablers. |
| Networking Reception | Hosted Cocktail & Executive Networking |
Jason Albuquerque, COO
Envision Technology Advisors
Jason Albuquerque is the Chief Operating Officer (COO) at Envision Technology Advisors, a veteran of the United States Marine Corps, and a nationally recognized voice in technology, operations, and cybersecurity leadership.
With over 25 years of experience across senior executive roles—including former Chief Information Officer (CIO) and Chief Security Officer (CSO)—Jason specializes in transforming IT and cybersecurity from traditional cost centers into core business enablers. At Envision, he leads company operations with a focus on building organizational cultures that are innovative, agile, resilient and secure by design.
A Certified Chief Information Security Officer (C|CISO) and Certified Government Chief Information Officer (CGCIO), Jason bridges the gap between complex risk environments and strategic business growth. He co-hosts the widely respected Business Security Weekly podcast, authors a cybersecurity column for Providence Business News, and speaks frequently on security leadership, risk governance, and digital transformation.
Jason maintains an active footprint in industry & public service leadership, always investing his time and effort in areas at the intersection of private industry, public policy, community service and workforce development.
His Honors & Recognition include Top Cybersecurity Leader (2021) – Security Magazine & (ISC)² Tech10 Lifetime Achievement Award – Rhode Island Monthly / RILIT, RI 40 Under Forty Award – PBN / and a 7-Time Solutions Award Winner – National Public Technology Institute
Manuel Lobao, Director of Cybersecurity & Compliance Services
Envision Technology Advisors
Drawing on more than 30 years of experience in technology and cybersecurity, Manuel Lobao is a recognized leader in information security, governance, risk management, and regulatory compliance. Throughout his career, he has demonstrated a proven ability to align people, processes, and technology to help organizations manage risk while enabling business growth and operational resilience.
As Director of Cybersecurity & Compliance Services at Envision Technology Advisors, Manuel leads cybersecurity advisory and compliance initiatives for organizations across healthcare, education, professional services, and other regulated industries. His work focuses on cybersecurity governance, risk assessments, security program maturity, regulatory compliance, incident response, and cyber resilience. He regularly advises executive leadership teams on navigating evolving threat landscapes, emerging technologies, and risk-based security strategies.
Manuel is responsible for helping organizations evaluate and strengthen security controls, identify and remediate gaps, and align cybersecurity investments with business objectives and regulatory requirements. His experience includes work with frameworks such as the NIST Cybersecurity Framework, NIST 800-53, HIPAA, CMMC, and emerging AI governance and risk management practices.
A Certified Information Systems Security Professional (CISSP), Certified Ethical Hacker (CEH), and Certified EC-Council Instructor, Manuel is passionate about developing the next generation of cybersecurity professionals through education, mentoring, and industry engagement. In recognition of his commitment to technology leadership and innovation, he was named a Rhode Island TECH10 Award recipient in 2020.
Daniel Howard, Systems Engineer, Service Provider MSSP
Fortinet
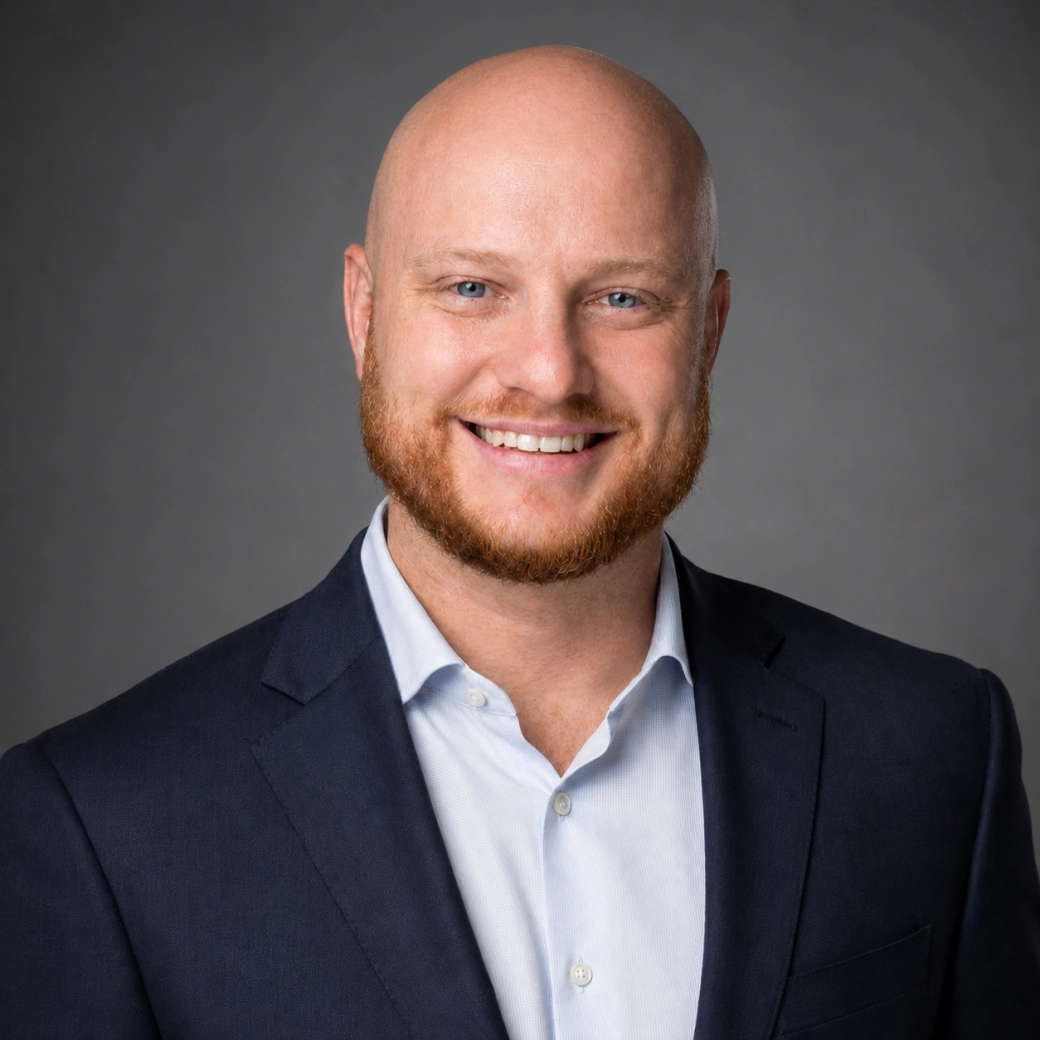
Daniel Howard is an MSSP Solutions Engineer at Fortinet, where he partners with Service Providers and Managed Security Service Providers to design and productize managed security services at a scale. With over a decade in cybersecurity across carrier, MSSP, and vendor environments, Daniel holds both the CISSP and Fortinet's NSE8 certification (#3255), placing him among fewer than a few hundred engineers worldwide to earn Fortinet's most rigorous credential.
He is the author of the Introduction to FortiGate NSE4 Study Guide series, a widely used reference in the Fortinet certification community. His current work centers on Universal SASE service creation, AI-driven security operations, and helping partners build profitable managed services in an increasingly complex threat landscape.
Daniel is based in North Carolina, where he lives with his wife and four children.
Linn F. Freedman CIPP/US, Chair Data Privacy, Cybersecurity + AI Practice
Robinson & Cole, LLP
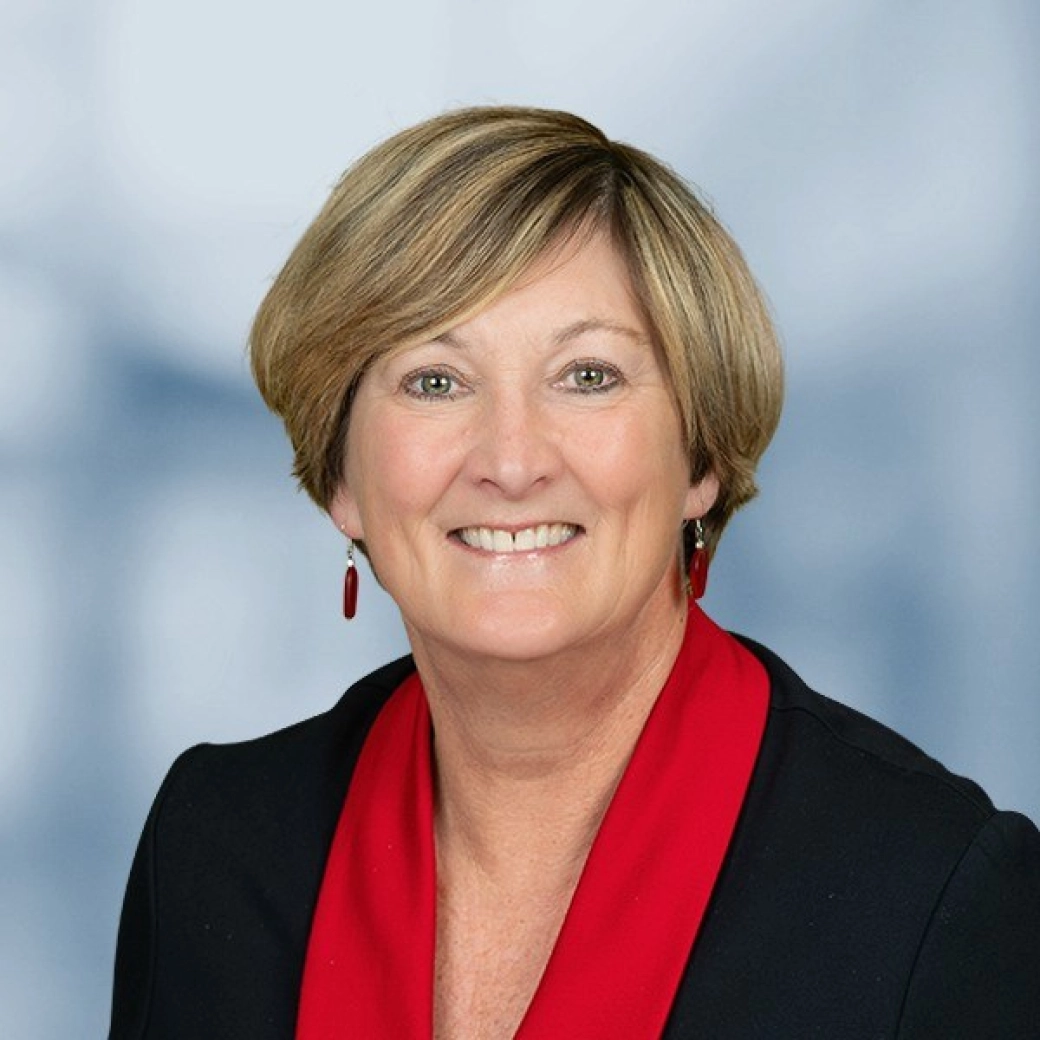
Linn Freedman is Chair of our firm’s Data Privacy + Cybersecurity practice and Chair of the AI Team. She focuses her practice on compliance with state and federal data privacy and security laws and regulations, emergency data breach response, mitigation, and litigation. She counsels clients on state and federal investigations and enforcement actions. She has a particular focus on health information technology and has assisted clients with navigating laws governing the access, use and disclosure of protected health information and substance use disorder information and HIPAA compliance. She is a Certified Information Privacy Professional. She is a former Deputy Chief of the Civil Division of the Rhode Island Department of Attorney General and has been practicing in data privacy and cybersecurity since 2003.
Linn is an Adjunct Professor at Roger Williams University School of Law teaching Privacy Law and a former Adjunct Professor in Brown University’s Executive Masters of Cybersecurity Program. She has been globally (since 2019) and nationally (since 2012) ranked in Chambers USA: America’s Leading Lawyers for Business in the area of Privacy Law since 2012, was named in among Becker’s Healthcare’s Women to Watch in Health IT to Know in 2020, 2022 and 2023, received the Lifetime Achievement Award as part of the 2023 Tech10 and Next Tech Generation Awards, presented by Rhode Island Monthly and the Tech10 Advisory Group, selected by her peers for inclusion in The Best Lawyers in America© and Super Lawyers, has been recognized by the National Law Review as a “Go-To Thought Leader” and by Lexology as a “Legal Influencer,” was named a Top Author and the #1 author in Cybersecurity in LexBlog’s JD Supra’s First Reader’s Choice awards in Cybersecurity every year since its launch in 2015, was named Health Data Management’s “Top 50 Healthcare IT Professionals in the US,” was named a “Director to Watch” by Directors & Boards, was recognized as one of 50 Top Healthcare IT Professionals by Health Date Management in 2015, was named Roger Williams University School of Law’s inaugural Champion of Justice in 2015, was named as Providence Business News Business Women Industry Leader for Professional Services and was a 2024 Leaders & Achievers honoree, was the recipient of the Rhode Island Department of Health Founder’s Award and Award for Excellence in Public Health Promotion, and was the recipient of the Rhode Island Attorney General’s Justice Award.
Linn serves on the Boards of Roger William University, the Rhode Island Center for Justice, and Professional Facilities Management. She is frequently interviewed and quoted in numerous publications including the The Wall Street Journal, National Public Radio, Modern Healthcare, Reuters and Bloomberg Law.
Linn has given presentations around the country on data privacy and cybersecurity, and she writes extensively on these topics, including for the firm’s Data Privacy + Security Insider and Health Law Diagnosis blogs.
Troy Damboise, CIA, CRMA
Liberty Bank
Troy is an Executive Vice President and Chief Risk Officer for Liberty Bank, the oldest and largest independent mutual bank in the country. Liberty is headquartered in Middletown, CT with 56 retail banking and loan production offices across Connecticut and Massachusetts. The Bank has over $9 Billion in assets and offers consumer and commercial banking, cash management, home mortgages, business loans, insurance and investment services.
As a member of the Executive Leadership Team, Troy oversees the Enterprise Risk Management Program and leads critical second line of defense functions, including Information Security, Vendor Risk Management, Regulatory Compliance, Bank Secrecy Act, Fair Banking/Lending, Corporate Security, Fraud Intelligence, Corporate Insurance, Incident Management, and Business Continuity. Previously, Troy was the General Auditor, directing the internal audit function and reporting to the Audit Committee of the Board of Directors.
Prior to joining Liberty, he spent fourteen years at ING U.S. as Vice President and Division Audit Director within ING Group Corporate Audit Services, where he managed audits for U.S. Retirement Plans, ING National Trust, Broker Dealers, Annuity businesses, and led a Compliance Risk Specialty Team.
Troy holds a Finance degree from Merrimack College and an MBA in Finance from Rensselaer Polytechnic Institute. He is a Certified Internal Auditor (CIA) and holds a Certification in Risk Management Assurance (CRMA).